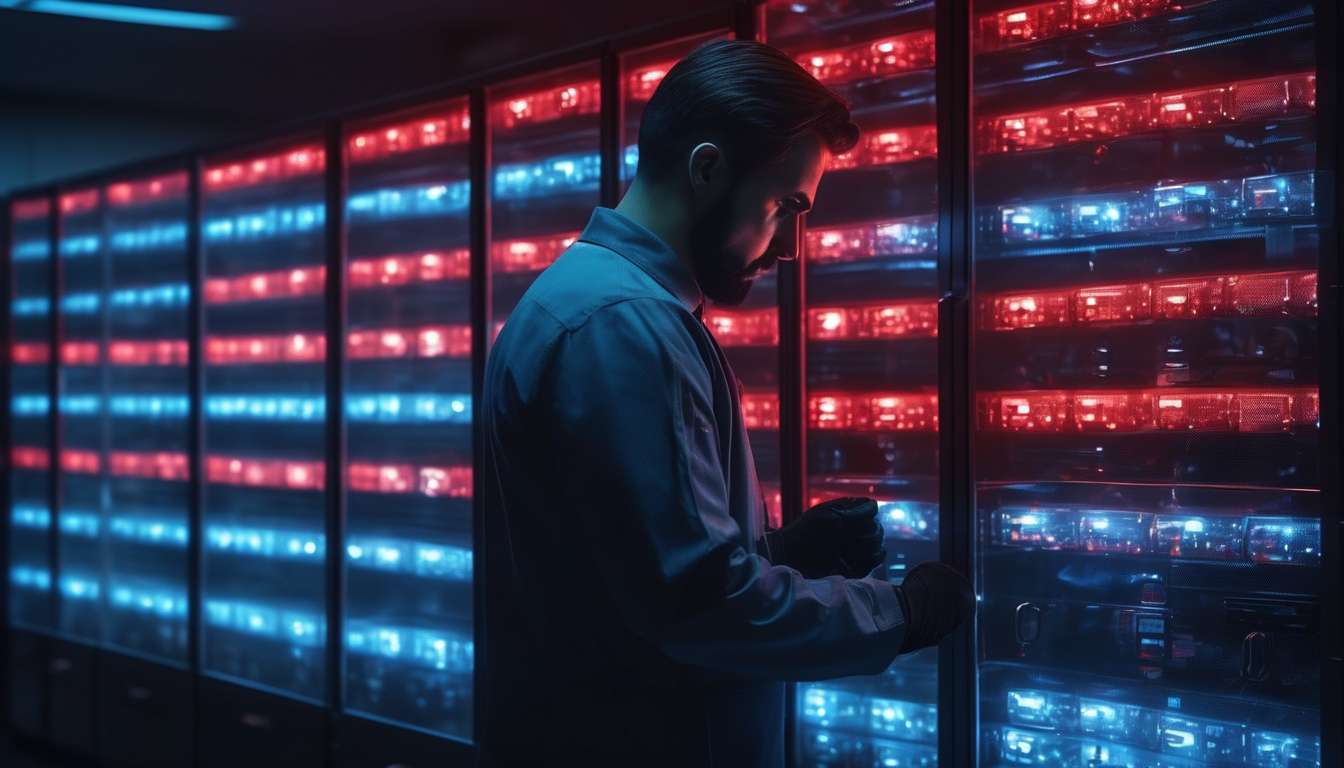
Knowing the night shift operator who once brought a box of printed spreadsheets into the server room, we remember how casually sensitive records were handled before our cybersecurity overhaul.
That close call—paper logs that could have revealed transaction patterns, staff schedules, and private correspondence—showed how a single oversight can expose data that, in our industry, can destroy reputations and livelihoods if revealed.
We redesigned our approach to safeguarding records for an adult-content company around four pillars:
- Physical controls
- Encrypted storage
- Vetted access pathways
- Rigorous incident response drills
As a team, we committed to policies that treat privacy as operational architecture rather than an afterthought.
Our approach balances compliance, usability, and the unique threats facing platforms that manage explicit material and personal data.
This article outlines the practical planning steps we implemented, the trade-offs we navigated, and the lessons other organizations can adopt to protect stakeholders while maintaining service continuity.
Risk Assessment Framework
We start by mapping assets, threats, and vulnerabilities unique to adult content companies so we can prioritize risks and focus our defenses where they matter most.
Key assets identified:
- Customer databases
- Payment records
- Creator content
- Backend systems
We score threats by likelihood and impact so everyone on the team sees what matters.
Practical technical controls we implement:
- Strong encryption for data at rest and in transit.
- Strict access control to limit who can see sensitive records (least privilege, role-based access).
- Network and service segmentation to reduce blast radius.
We do not treat security as optional; instead we build processes and response capabilities.
Incident response planning and exercises:
- Define roles and responsibilities (who does what).
- Establish escalation paths and communication channels.
- Set recovery objectives (RTO/RPO) and containment strategies.
- Run tabletop exercises and drills to validate plans.
- Adjust controls and update documentation based on lessons learned.
By aligning technical safeguards with shared responsibility and transparent processes, we:
- Strengthen internal trust.
- Protect members’ privacy and livelihoods.
- Maintain continuity through documented decisions and practiced response.
Physical Security Measures
We secure physical premises and hardware through layered controls.
Controlled entry, surveillance, asset inventory, and environmental protections work together to reduce theft, tampering, and downtime.
We insist on consistent access control protocols so every team member knows their role and feels trusted.
- Access controls: badge systems, visitor logs, and timed door locks limit exposure while promoting shared responsibility.
- Accountability: clear protocols ensure everyone understands permitted access and escalation paths.
We maintain an up-to-date hardware inventory and label devices.
- Regular audits: scheduled checks prevent assets from drifting untracked.
- Labeling and inventory alignment: keep teams coordinated and accountable for devices.
We protect server rooms with environmental and power controls.
- Environmental sensors: monitor temperature, humidity, and water intrusion.
- Power resilience: UPS and redundant power maintain service availability.
We integrate physical alerts into incident response workflows.
- Alerting: physical alarms trigger documented escalation, containment, and recovery steps.
- Workflow integration: ensures coordinated, auditable responses across teams.
We keep physical safeguards complementary to data protection and foster a security culture.
- Separation of concerns: physical controls are distinct from encryption, but they prevent adversaries from reaching devices that hold sensitive keys or records.
- Culture: encourage everyone to contribute to protecting shared spaces and maintaining trust.
Data Encryption Strategy
Encryption coverage:
We’ll encrypt sensitive content and metadata both at rest and in transit using proven algorithms and key management practices.
Standardize on strong ciphers and reviews:
We’ll standardize on strong, industry-vetted ciphers and perform regular cryptographic reviews so everyone feels confident their work is protected.
Key management and rotation:
We’ll rotate keys on a schedule and store them in hardened vaults to reduce single points of failure.
We’ll document key lifecycles so team members can follow consistent procedures.
Integration with access control:
We’ll integrate data encryption with our broader access control model, ensuring encrypted blobs are only decryptable by authorized services and roles.
Logging and accountability:
We’ll log decryption events to support transparency and collective accountability.
Testing and drills:
We’ll run routine drills that include simulated breaches to validate encryption boundaries and feed results into our incident response playbook.
Cross-team learning:
We’ll share learnings across teams so operators, developers, and managers belong to a single security-minded community.
Operational mindset:
By treating encryption as a maintained, auditable capability rather than a one-time setup, we’ll keep content and metadata secure while staying ready to respond if an event occurs.
Access Control Policies
We’ll define granular role-based and attribute-based policies that ensure only authorized people and services can view, modify, or distribute sensitive content and metadata.
We’ll map roles to least-privilege permissions, require multi-factor authentication, and enforce time- and context-bound access so every team member feels included in protecting our community’s content.
Access control rules will tie to identity proofs and attributes like job function, project, and clearance level, reducing accidental exposure.
We’ll integrate logging that records who accessed what and when, feeding into incident response playbooks so we can act quickly and transparently if something goes wrong.
Access decisions will reference strong data encryption status — denying access if data is at risk or keys are compromised.
We’ll regularly review and certify permissions with the people affected, welcome feedback, and run tabletop exercises together.
That way, we maintain clear, accountable access control while fostering trust, belonging, and shared responsibility across the organization.
Secure Storage Architecture
Design goal: segment sensitive content and metadata; enforce strong encryption; isolate keys and backups to minimize blast radius.
We’ll group assets by sensitivity and apply least-privilege access control so team members only reach what they need.
Store content in separated buckets or databases with distinct IAM roles, network policies, and audit logging so compromise is contained and traceable.
Implement robust data encryption using proven algorithms and managed key services, keeping keys off general application hosts and rotating them regularly.
Backups will be encrypted, segmented, and stored in a separate trust domain with strict retrieval procedures.
Integrate storage telemetry with monitoring to detect anomalies quickly and ensure logs are immutable.
Document responsibilities and escalation paths so everyone understands their role in preserving privacy and integrity.
- Define clear ownership for: encryption keys, backup custody, access control administration, and audit log review.
- Establish incident response playbooks with step-by-step retrieval, key compromise procedures, and communication templates.
- Schedule regular audits and tabletop exercises to validate controls and team readiness.
This approach builds a shared sense of stewardship, where data encryption, access control, and coordinated incident response planning reinforce a safer environment we all belong to.
Incident Response Playbook
We will maintain a tested incident response playbook that assigns clear roles, defines step-by-step actions for common scenarios (including key compromise and content exposure), and prescribes communication and containment procedures to minimize harm.
We will document procedures for detection, triage, containment, eradication, recovery, and post-incident review so everyone knows their part and feels supported.
We will integrate technical controls into response steps, including:
- Data encryption (at rest and in transit)
- Robust access control and least-privilege principles
- Rapid rotation of keys and credentials
- Immediate revocation of compromised tokens
We will script evidence collection and system snapshots to preserve forensic integrity while protecting member privacy.
We will provide internal and external communication templates that respect legal and community expectations without amplifying risk.
We will run regular tabletop exercises and simulated incidents with cross-functional teams, then update the playbook based on lessons learned.
We will track metrics such as:
- Time to detect
- Time to contain
- Time to restore services
We will commit to transparency with stakeholders while safeguarding sensitive details, reinforcing trust and a shared commitment to protecting our community.
Compliance and Audit Processes
We’ll establish regular compliance and audit processes that verify legal, regulatory, and platform-specific requirements are met and that our security controls work as intended.
We schedule periodic internal and external audits so everyone knows we’re accountable and included in protecting our community.
Auditors review data encryption practices, assess key management, and confirm that encrypted backups and transit protections meet industry standards.
We test access control mechanisms to ensure least-privilege models are enforced, role mappings are accurate, and orphaned accounts are removed promptly.
Audit trails and logs are retained with tamper-evident controls so reviewers can trace actions without fearing exclusion from findings.
We integrate compliance checks into our change management and vendor assessments, ensuring third parties uphold equivalent protections.
We validate that incident response procedures are aligned with legal obligations and contractual reporting timelines, using post-incident audits to close gaps.
By treating audits as collaborative improvement exercises, we build trust, strengthen safeguards, and reinforce that every team member plays a role in maintaining our shared security posture.
Employee Training Programs
We’ll provide role-specific, recurring cybersecurity training that teaches employees how to safely handle sensitive content, recognize threats, and follow our policies.
We design clear modules so everyone feels included and capable, whether they’re content moderators, developers, or HR.
Topics covered include:
- Data encryption best practices
- Strong password hygiene
- Multi-factor authentication
We map controls to daily tasks so staff see relevance and can apply safeguards in their workflows.
We teach strict access control principles so teammates understand least-privilege, provisioning, and timely deprovisioning.
Benefits:
- Reduces accidental exposure
- Builds mutual trust across teams
We run tabletop exercises and hands-on labs that simulate breaches and practice incident response steps.
Goals:
- Make response roles and communications familiar before an event
- Improve practical skills under realistic conditions
We assess comprehension with short tests and real-world drills, then iterate training based on feedback and audit findings.
We document outcomes, measure improvements, and celebrate competence to create a shared-responsibility culture where protecting records is a collective, practiced commitment.
How does the company handle third-party vendors that process or host user-submitted adult content, and what contractual safeguards are in place to ensure they meet the same cybersecurity standards?
Vendor selection and vetting
We vet third‑party vendors thoroughly before engaging them, including reviewing security posture, compliance history, privacy practices, and reputation. Vendors that process or host user‑submitted adult content must demonstrate appropriate controls and a commitment to user safety.
Certifications and technical controls
We require SOC 2 or equivalent certifications (or evidence of comparable, measurable controls). We also mandate:
- Encryption of data in transit and at rest.
- Strict access controls and least‑privilege principles.
- Multi‑factor authentication for administrative access.
Contractual requirements
We include contract clauses that require:
- Incident notification with defined timelines.
- Audit rights and the ability to review security controls.
- Clear data deletion and retention procedures.
- Breach liability and remediation responsibilities.
Ongoing verification and accountability
We require regular security assessments (e.g., penetration tests, vulnerability scans) and periodic evidence of continued compliance. We enforce employee training standards for vendors that handle sensitive content.
Enforcement and termination
If a vendor fails to meet our requirements or demonstrate remediation, we will terminate the relationship or require corrective action within agreed timelines.
Collaboration and user safety
We work collaboratively with vendors to maintain legal compliance and keep users safe and respected, balancing strong protections with operational needs.
What privacy-preserving measures are used to minimize retention of highly sensitive metadata (e.g., upload timestamps, device identifiers, geolocation) that could inadvertently identify contributors or subjects?
Minimize collection to what’s strictly necessary.
- Collect only the metadata fields required for the feature or analysis.
- Avoid collecting optional identifiers unless they provide clear, documented value.
Anonymize or transform identifiers.
- Hash or pseudonymize device IDs and user identifiers with salted, rotating keys.
- Remove or generalize persistent identifiers before they leave the client or enter analytic stores.
Reduce timestamp precision.
- Truncate or bucket timestamps (for example, to minutes, hours, or days) to prevent exact event reconstruction.
- Use coarse time windows for analytics when high precision isn’t required.
Coarsen geolocation data.
- Strip precise GPS coordinates and map to coarse regions (city, county, or grid cells).
- Only capture finer location when strictly necessary and with explicit justification.
Limit retention with automated audits and deletions.
- Implement short, auditable retention windows aligned to business need.
- Enforce automatic deletion once data reaches retention end-of-life.
Apply statistical privacy techniques.
- Use differential privacy or other noise-injection methods where feasible to protect aggregate outputs.
- Prefer aggregated, non-identifying reports over raw data access.
Enforce strict access controls and logging.
- Restrict queries to authorized teams and roles with least-privilege access.
- Log all access and queries to metadata stores and audit regularly.
Prefer aggregated, non-identifying queries.
- Allow teams to query aggregated metrics rather than raw records.
- Implement query vetting and output controls to prevent re-identification.
If you’d like, I can convert these into a short checklist, a policy template, or suggested technical implementations (e.g., example hashing schemes, retention policies, or differential privacy libraries).
Are there special protocols for handling legal requests (subpoenas, warrants, DMCA takedown notices) specific to adult content, and how is user notification and data minimization handled in those cases?
We handle legal requests for adult content with extra care.
We follow the law while minimizing scope. We comply with lawful requests but always seek to limit the breadth of information produced.
We challenge overbroad subpoenas and require specific court orders for identifying data. Requests that lack sufficient specificity are opposed or narrowed; identifying user data is only produced in response to explicit judicial orders.
We notify users unless prohibited. When allowed, we inform contributors about requests affecting their content and provide them an opportunity to respond.
We seek narrower production and redact unrelated information. Produced materials are restricted to what is strictly relevant, and unrelated or irrelevant data are redacted.
We retain only essential records and purge sensitive metadata per policy. Nonessential logs and metadata are removed according to retention and privacy rules.
We log all requests for accountability. Every legal request and response is recorded to ensure transparency and enable review.
We are committed to protecting contributors and building trust while complying with legal obligations. Our priority is safeguarding user privacy and integrity while fulfilling lawful duties.
Conclusion
You’ve built a strong, practical cybersecurity plan that fits the unique risks of an adult content company.
By assessing threats, hardening physical and digital defenses, encrypting data, and enforcing strict access controls, you’ll reduce exposure.
Secure storage, a clear incident response playbook, regular audits, and ongoing employee training keep protections current and accountable.
Stay vigilant, review controls frequently, and adjust procedures as the threat landscape and compliance requirements evolve.